Threat Intelligence
Tor browser privacy risks and the reality of anonymous browsing
Anonymity networks mask your destination from local observers, but they expose your traffic to active manipulation at the network edge.
Threat Intelligence coverage from RedTeam Monitor holds 20 articles, 19 of them reference guides. The newest was published on October 19, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include MITRE D3FEND and CISA Cybersecurity Advisories.
Anonymity networks mask your destination from local observers, but they expose your traffic to active manipulation at the network edge.
Federal authorities announced actions against North Korean schemes that used stolen US identities to infiltrate more than 70 American companies and earn millions.
Most breaches succeed because defenders focus on perimeter entry rather than detecting lateral movement inside the network after the initial compromise occurs.
Raw indicators lack context, so enrichment adds historical and structural data that turns noise into actionable intelligence for security teams.
Static IOCs miss modern threats that leave no files, so you must pair them with behavioral detection to catch living-off-the-land attacks before data exfiltration begins.
Nation-state hackers operate like foreign intelligence agencies, using slow, patient infiltration to steal secrets rather than quick, loud thefts.
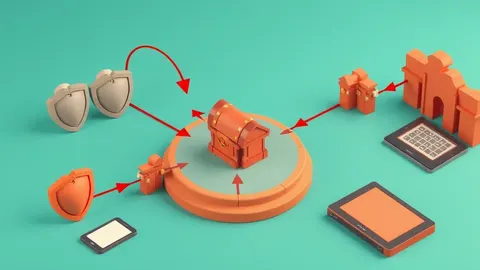
Red teaming reveals hidden gaps by simulating full adversary campaigns, exposing how small weaknesses chain together to bypass layered security controls.
Sigma rules abstract detection logic from specific log formats, allowing security teams to share threat hunting strategies across any security information and event management platform.
ASN analysis reveals the infrastructure owners behind attacks, allowing teams to block entire networks rather than chasing individual IP addresses.
The Navigator turns abstract threat data into a visual heatmap, revealing which attacker behaviors your defenses actually catch and which slip through unnoticed.
Operational threat intelligence bridges the gap between raw data and action by telling you exactly what to block and when to investigate.
Attackers bypass security by using legitimate system tools already present on your device, making detection nearly impossible without behavioral analysis.
Persistence relies on the operating system’s trust in its own configuration files, turning standard administrative features into reliable backdoors that survive reboots and credential changes.
Strategic intelligence shapes long-term risk budgets and architecture, while tactical intelligence drives immediate detection rules and incident response playbooks.
Most small organizations waste resources on raw data feeds they cannot process, while ignoring the high-value context that actually stops breaches.
Initial access brokers leave distinct digital fingerprints in credential logs and external communication patterns that standard alerts often miss because they mimic legitimate administrative activity.
Canary tokens generate noise by triggering external callbacks, which helps distinguish attacker noise from background traffic but fails against isolated networks.
Public data reveals attacker infrastructure before intrusion, allowing defenders to block threats at the network edge rather than chasing internal indicators.
Deception technology turns your entire network into a sensor by placing fake assets that trigger alerts only when an attacker touches them.
Attackers hide in plain sight by abusing trusted system tools, making behavioral anomalies the only reliable detection signal for your security operations.