Most teams confuse business continuity with disaster recovery, treating data restoration as the only goal while ignoring the operational steps that keep services alive during an outage.
Scanners find configuration errors and missing patches, but they cannot detect logic flaws or custom code errors that require human reasoning to exploit.
Most breaches originate from compromised credentials rather than external hackers, making identity verification the primary defense layer against data loss.
Most identity theft occurs through credential reuse and weak recovery flows, not through direct system breaches or sophisticated malware campaigns targeting your device.
The OWASP Top 10 is not a coding checklist but a shared language for risk, yet most teams treat it as a static list rather than a dynamic map of attacker behavior.
Digital forensics treats hard drives like crime scenes, where deleted files leave magnetic traces that reveal hidden actions and timelines long after the event.
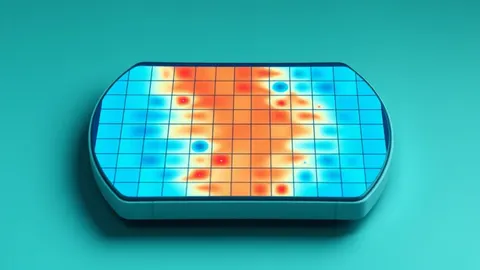
The Navigator turns abstract threat data into a visual heatmap, revealing which attacker behaviors your defenses actually catch and which slip through unnoticed.
EDR shifts security from static file matching to behavioral analysis, but it introduces significant system overhead and alert fatigue that many teams underestimate.
Password spraying hides in plain sight by staying below lockout thresholds, making detection dependent on log correlation rather than single-event alerts.
Single sign-on shifts trust from local password checks to signed cryptographic tokens, creating a single point of failure that centralizes both access and attack surfaces.
Secrets managers do not encrypt data at rest by default; they shift the risk from storage to the authentication protocol and the client-side runtime environment.
Zero-day malware bypasses defenses by exploiting unknown flaws, making signature-based detection useless until the vulnerability is patched and signatures are updated.
Unauthenticated dashboard access often bypasses network controls, giving attackers direct control over cluster resources without triggering standard intrusion alerts.
Security groups act as stateful virtual firewalls that filter traffic at the instance level, preventing unauthorized access before it reaches your application code.
Small teams can block most impersonation attempts by publishing a single text record in their DNS zone, requiring no new software or hardware purchases.
Attackers bypass security by using legitimate system tools already present on your device, making detection nearly impossible without behavioral analysis.